When a new piece of software touches anything connected to a hospital network, IT security needs a fast, structured way to evaluate it — not a forty-page vendor whitepaper, and not a verbal assurance on a sales call. A CMMS in particular touches asset data, technician identities, vendor access, and sometimes building automation systems, which gives it a wider surface than most point solutions. This checklist breaks the review into four categories so your team can work through it the same way during every vendor evaluation. Start a free OxMaint trial and run this checklist against a live system instead of a sales deck.
On-Premise Deployment · Security Checklist · Healthcare IT
A 23-Point Security Review for Any Healthcare CMMS
Use this checklist to evaluate access control, data handling, integrations, and deployment options before approving a maintenance platform for hospital-wide use.
Category 1
Access Control
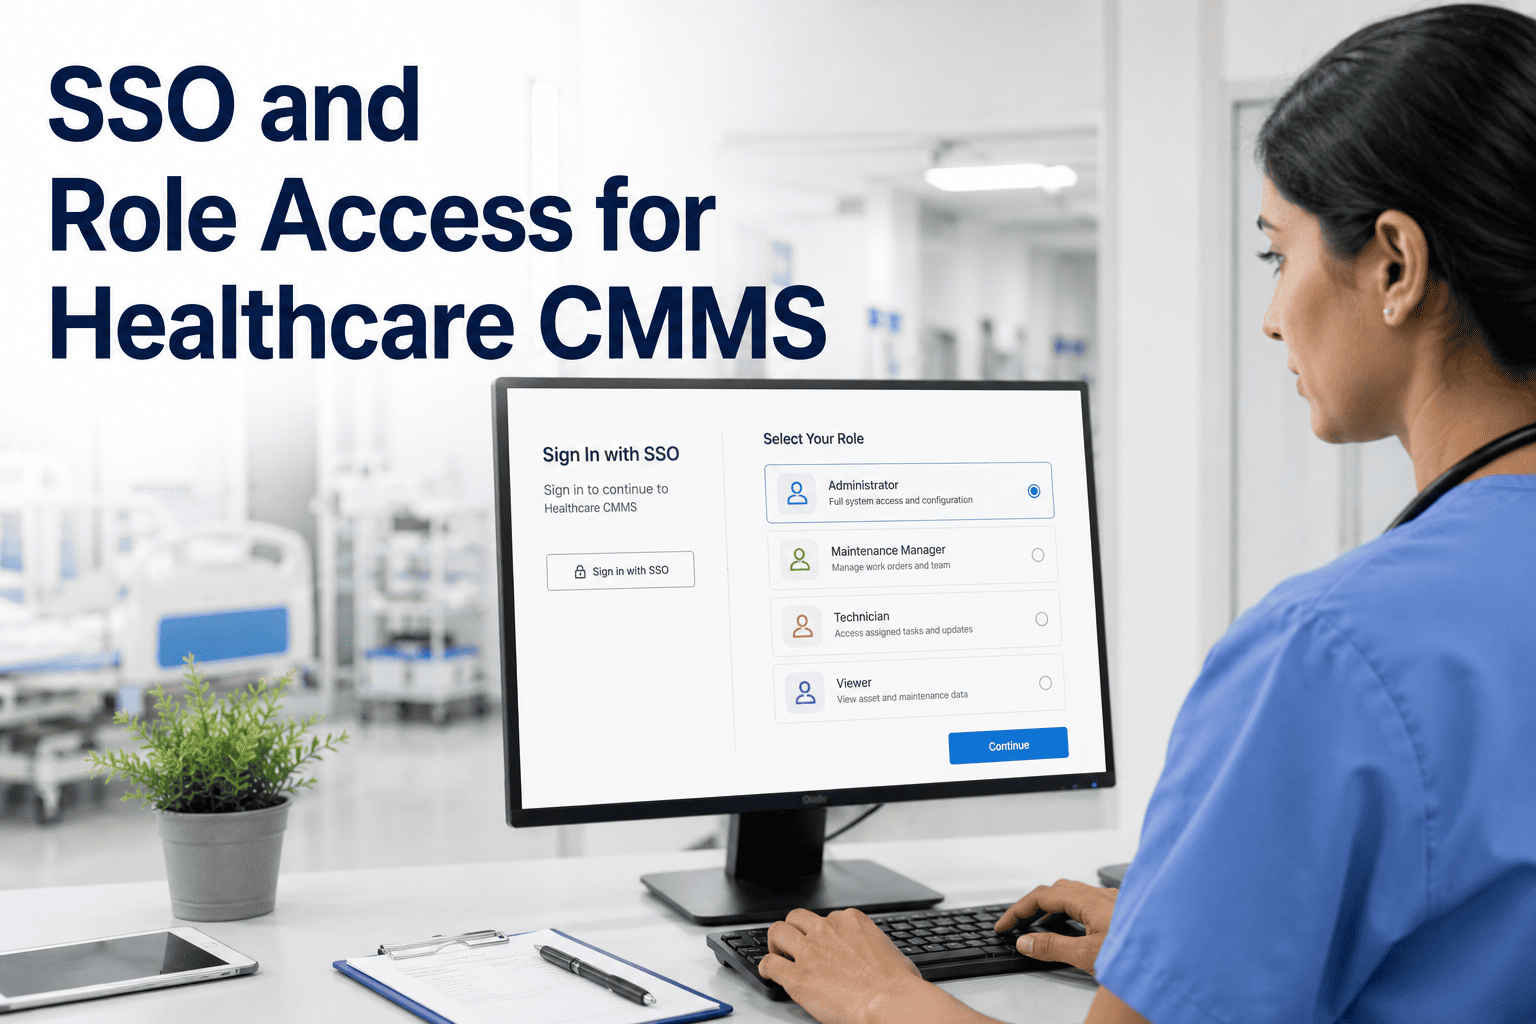
Single sign-on supported through your existing identity provider
Role-based permissions limit each user to their job function
Vendor and contractor accounts can be scoped to a single work order
Multi-factor authentication available and enforceable by policy
Account deactivation removes access immediately, not on a delay
Every login and permission change is captured in an audit log
Category 2
Data Handling
Data encrypted both in transit and at rest
Clear documentation of where asset and technician data is stored
Backup and retention policy documented and available for review
Data export available in a standard, non-proprietary format
Clear data ownership and deletion terms if the contract ends
OxMaint · Security Review · Healthcare CMMS
Run This Checklist Against a Real System, Not a Slide Deck
See how OxMaint answers every item on this list during a live walkthrough with your security and IT team.
Category 3
Integrations
API access documented and available for ERP and BI connections
IoT and building automation integration does not require open inbound ports
Third-party integrations are scoped to specific data, not full access
Integration credentials are rotatable without a full system reconfiguration
Vendor maintains a documented list of subprocessors and data flows
Mobile app syncs over encrypted channels, including in offline mode
Category 4
Deployment
On-premise or private cloud deployment available if required
Update and patch schedule can be controlled by your own IT team
Disaster recovery plan documented with a defined recovery time
Network architecture diagram available for security review
Vendor has a documented incident response and breach notification process
Compliance documentation available for relevant healthcare standards
Why This List Exists
What Skipping This Review Tends to Cost
$7M+
Average cost of a healthcare data breach today
1 in 3
Healthcare breaches connected to third-party vendor access
230+ days
Average time to identify and contain a healthcare breach
Expert Review
What an IT Security Lead Looks for First
PR
The access control category is where most vendors lose us. If a maintenance platform cannot scope a contractor to a single work order, it does not matter how good the rest of the feature set is — it does not pass review.
P. Rao
IT Security Lead, multi-site hospital group
Frequently Asked Questions
Healthcare CMMS Security Review — Common Questions
Can I get this checklist as a document to share with my security team?
Does OxMaint provide documentation for each of these items?
Yes. Security documentation, architecture diagrams, and compliance materials are available on request for IT and security teams conducting a formal review.
Request the full documentation package.
How long does a typical security review take?
Most hospital IT teams complete an initial review using a checklist like this one within a single meeting, with deeper technical questions following over one or two additional calls.
Is this checklist specific to OxMaint or usable for any vendor?
The categories and items apply to any healthcare CMMS evaluation, regardless of vendor, since they reflect the access, data, integration, and deployment questions every hospital IT team needs answered.
OxMaint · Healthcare CMMS · Free to Start
See How OxMaint Answers Every Item on This List
Walk through access control, data handling, integrations, and deployment with our team before you sign anything.